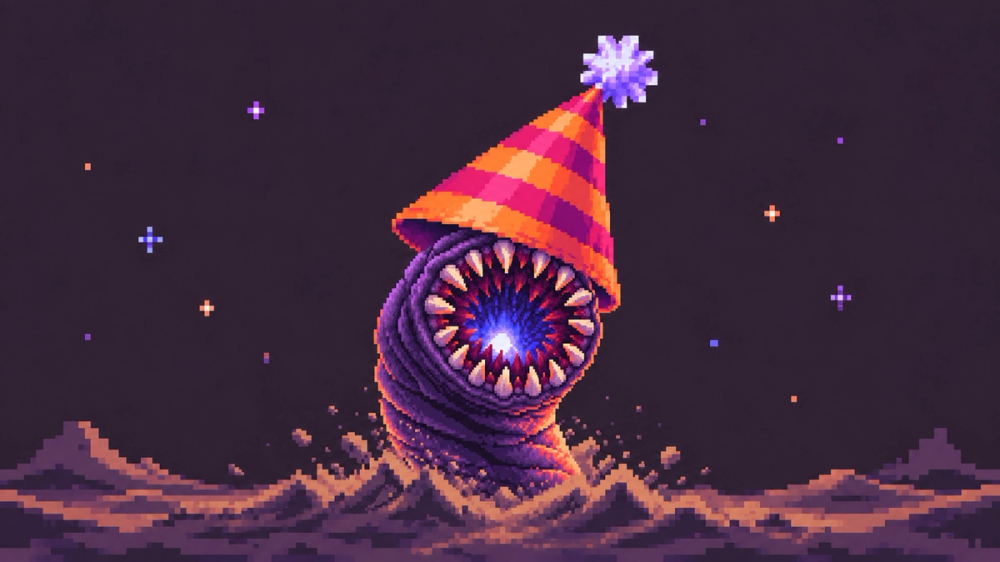
Happy Birthday, Shai-Hulud
Socket ·
This week marks one year since an attacker pushed a malicious version of @ctrl/tinycolor to npm, kicking off the worst year for npm security on record. At the time, the package was downloaded more than two million times a week. Within a day the same code was spreading on its own across dozens of packages, and then into CrowdStrike's npm namespace. It was the first known self-propagating worm in the npm ecosystem, and it has not really stopped since. The tinycolor compromise put software supply…
Soutenez Socket en consultant la ressource originale
Lire l'article original