Flux
Couleur d'accent
Toutes les sources

Socket

174 articles Flux RSS
Cybersécurité Programmation
PHP Foundation Says Chainguard Broke Security Embargo Ahead of Emergency Patches Nouveau

PHP Foundation Says Chainguard Broke Security Embargo Ahead of Emergency Patches

The PHP Foundation says Chainguard broke a coordinated security embargo by releasing patched PHP container images hours ahead of schedule, making the fix available for attackers to study while other distributors were still preparing updates. In a postmortem published October 21, the Foundation described a disclosure process disrupted by leaked CVE identifiers, an accidentally published exploit demonstration, and Chainguard’s decision to release early. It also acknowledged that work on the…

Socket
PHP Patches Critical RCE Vulnerabilities, Organizations Urged to Take Unpatched Sites Offline Nouveau

PHP Patches Critical RCE Vulnerabilities, Organizations Urged to Take Unpatched Sites Offline

Organizations running internet-facing PHP applications have been advised to take them offline if they cannot immediately patch two critical vulnerabilities. That is how bad this is: the NSA recommended taking affected systems offline until they can be fully mitigated, while CERT-EU urged organizations unable to patch to consider isolating their applications from public networks. The patches are now available. PHP released emergency updates on October 21, fixing flaws that can let attackers…

Socket
LiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI Credentials Nouveau

LiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI Credentials

LiteLLM 1.107.0 delivers a credential stealer through Python startup hooks, while container build provenance points to a lookalike source repository used by the project’s release workflow. LiteLLM version 1.107.0 contains malicious Python startup files that collect cloud credentials, private keys, browser data, and authentication files for AI development tools. Socket’s AI scanner flagged the seven distributed wheels seven minutes after publication, and static analysis confirms both a…

Socket
vlt 1.5.0 Adds Agent Skills Management Récent

vlt 1.5.0 Adds Agent Skills Management

JavaScript packages increasingly ship instructions for coding agents alongside their code. But installing a package doesn’t necessarily put those instructions somewhere an agent will find them. Developers can end up copying skill files into their projects by hand, then having to keep those copies current as dependencies change. vlt 1.5.0 brings that work into the package manager. Its new vlt skills command discovers skills in installed dependencies and links them into the directories coding…

Socket
Rust 1.100 Will Add Dependency Cooldowns to Cargo Récent

Rust 1.100 Will Add Dependency Cooldowns to Cargo

Rust developers will soon be able to tell Cargo to wait before adopting newly published dependencies. Rust 1.100, scheduled for November 12, will bring stable support for a configurable minimum publish age, letting teams delay dependency updates to give researchers and maintainers time to detect malicious releases before more projects pull them in. The stabilization PR merged on August 28, and Rust’s draft release notes list the feature for 1.100. The setting is available on beta but has not…

Socket
Deno Goes the Way of the Dinosaur

Deno Goes the Way of the Dinosaur

Cloudflare is acquiring Deno’s team, but the deal comes with an unwelcome surprise for developers who built on its JavaScript and TypeScript runtime: the company is winding down development, leaving the community to work out how to keep it going. Ryan Dahl, creator of both Node.js and Deno, announced on October 9 that the entire team is joining Cloudflare. Deno will receive another year of monthly bug fixes and security updates before the team ends its development work. Deno Deploy will shut…

Socket
Anthropic Gives Open Source Maintainers a Fast Track to Mythos Vulnerability Findings

Anthropic Gives Open Source Maintainers a Fast Track to Mythos Vulnerability Findings

Anthropic has launched OSS Scanner, a free, opt-in service that uses its strongest Claude models, including Mythos, to look for vulnerabilities in open source projects. Participating maintainers receive reports showing how to reproduce the vulnerabilities, along with proposed fixes when available, without waiting for Anthropic’s researchers to review the findings. The reviewers have struggled to keep up with the volume of reports. Over six months, the company says it found more than 29,000…

Socket
Front Lines Podcast: What Founders Get Wrong When Pitching CISOs

Front Lines Podcast: What Founders Get Wrong When Pitching CISOs

“It’s never been easier to build a security program. It’s never been harder to secure an organization.” Socket CISO Andrew Becherer recently appeared on Early Adopters: CISO. Recorded at Black Hat 2026, the conversation explores how security leaders build programs, evaluate new technology, and decide which vendors to trust as AI accelerates both development and the work of securing it. Becherer draws on his experience building security programs at companies including Datadog, where he joined as…

Socket
 Socket for Origin Now Available

Socket for Origin Now Available

Socket for Origin is now available in the Origin App Marketplace, with automatic dependency scans and security findings directly on your pull requests. SpaceXSI built Origin to give developers and AI agents a place to host and collaborate on code at a scale traditional Git infrastructure wasn’t designed for. Socket adds dependency security to that workflow, helping teams catch risky packages and compromised updates in pull requests before they merge. We’re joining more than 20 developer tools…

Socket
Agent Baseline Publishes Security Reference Architecture for Software Factories

Agent Baseline Publishes Security Reference Architecture for Software Factories

Agents now write a large share of the code at some of the biggest engineering organizations. Uber says more than 70% of its pull requests are attributed to local or cloud agents, and its weekly agent requests grew 9.4 times between February and August. Stripe’s internal coding agents, which it calls Minions, write more than a thousand of the pull requests Stripe merges each week, and engineers can start one from a Slack message. Vercel’s factory for maintaining its AI SDK authored 25 to 35% of…

Socket
arXiv Is Rate Limiting Authors Following a Flood of AI Slop Submissions

arXiv Is Rate Limiting Authors Following a Flood of AI Slop Submissions

Low-quality submissions are overwhelming arXiv’s volunteer moderators and delaying quality papers for days or weeks. The preprint repository is now limiting each submitter to two submissions per calendar month. The new policy, effective this month, applies across all subject categories. It adds a monthly cap to an existing limit of three active submissions at a time, in place since 2024. Rejected papers count toward the monthly total, too, since a paper that gets bounced has already consumed a…

Socket
New GhostAction Wave Hits Hundreds of Repos, Expanding Beyond CI/CD Secrets to Cloud Credentials

New GhostAction Wave Hits Hundreds of Repos, Expanding Beyond CI/CD Secrets to Cloud Credentials

Update (October 9, 2026, [HH:MM] UTC): Since publication, Socket has identified more than 500 GitHub accounts that committed the malicious workflow to tens of thousands of repositories since October 7, 2026, including several organization-owned ones reached through the compromised contributors. The two accounts described below remain the most prominent, and kitao/pyxel is the clearest confirmed case of publishing credentials being targeted by a successful run. Socket analyzed an October 8, 2026…

Socket
TensorLake npm SDK Compromised in ChainDrop Shai-Hulud Credential-Stealing Attack

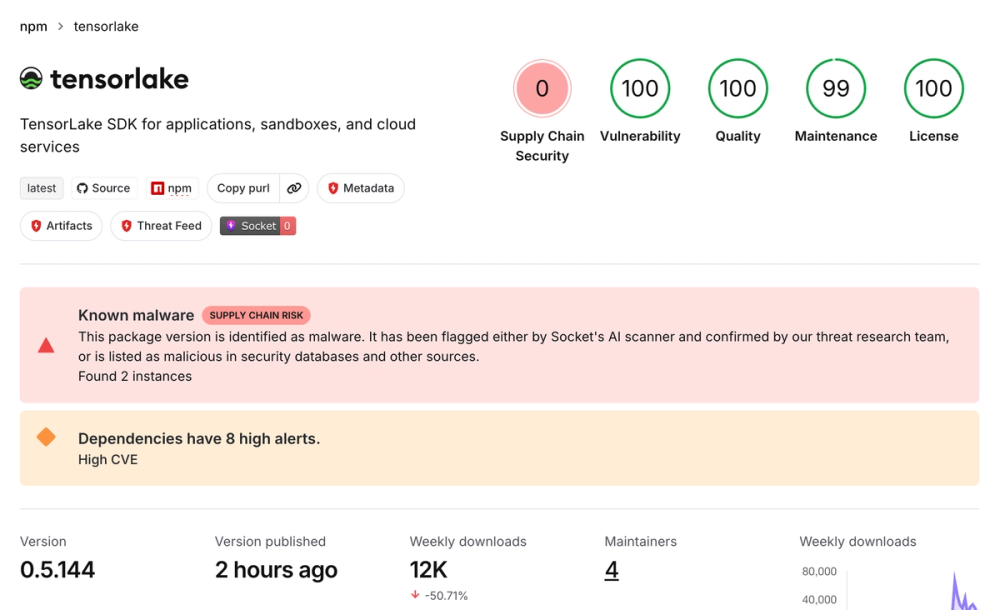
TensorLake npm SDK Compromised in ChainDrop Shai-Hulud Credential-Stealing Attack

Socket detected a compromised release of tensorlake, the npm SDK for Tensorlake’s AI agent infrastructure, in a ChainDrop / Shai-Hulud supply chain attack. Version 0.5.144 contains obfuscated malware that harvests credentials, exfiltrates secrets, establishes persistence, and executes remotely supplied code. The package receives approximately 12K weekly downloads and has over 1k stars on GitHub. Tensorlake provides isolated sandboxes for running untrusted, LLM-generated code, with…

Socket
16 Malicious Firefox Extensions Steal Cryptocurrency Wallet Credentials

16 Malicious Firefox Extensions Steal Cryptocurrency Wallet Credentials

Socket Threat Research identified a coordinated campaign of 16 Firefox extensions targeting cryptocurrency wallet users. The extensions masquerade as wallet portals, desktop utilities, and browser tools, but their code intercepts recovery phrases and private keys during wallet import flows and attempts to send those secrets to attacker-controlled Cloudflare Workers. The campaign is a cryptocurrency wallet credential-stealing operation with a variety of lures: Four large extensions are clones of…

Socket
Introducing Socket Scanning for VS Code Marketplace Extensions

Introducing Socket Scanning for VS Code Marketplace Extensions

If 2026 has shown us anything, it’s that the software supply chain doesn’t stop at the dependencies in your apps. It includes the tools your developers use to write, build, and ship code. VS Code extensions run inside an environment full of source code, credentials, and access to company infrastructure. A malicious extension can put all of that within an attacker’s reach. Today, we’re launching experimental support for scanning VS Code Marketplace extensions. This extends our proactive security…

Socket
Esc