Flux
Couleur d'accent
Long-Running Agents

Long-Running Agents

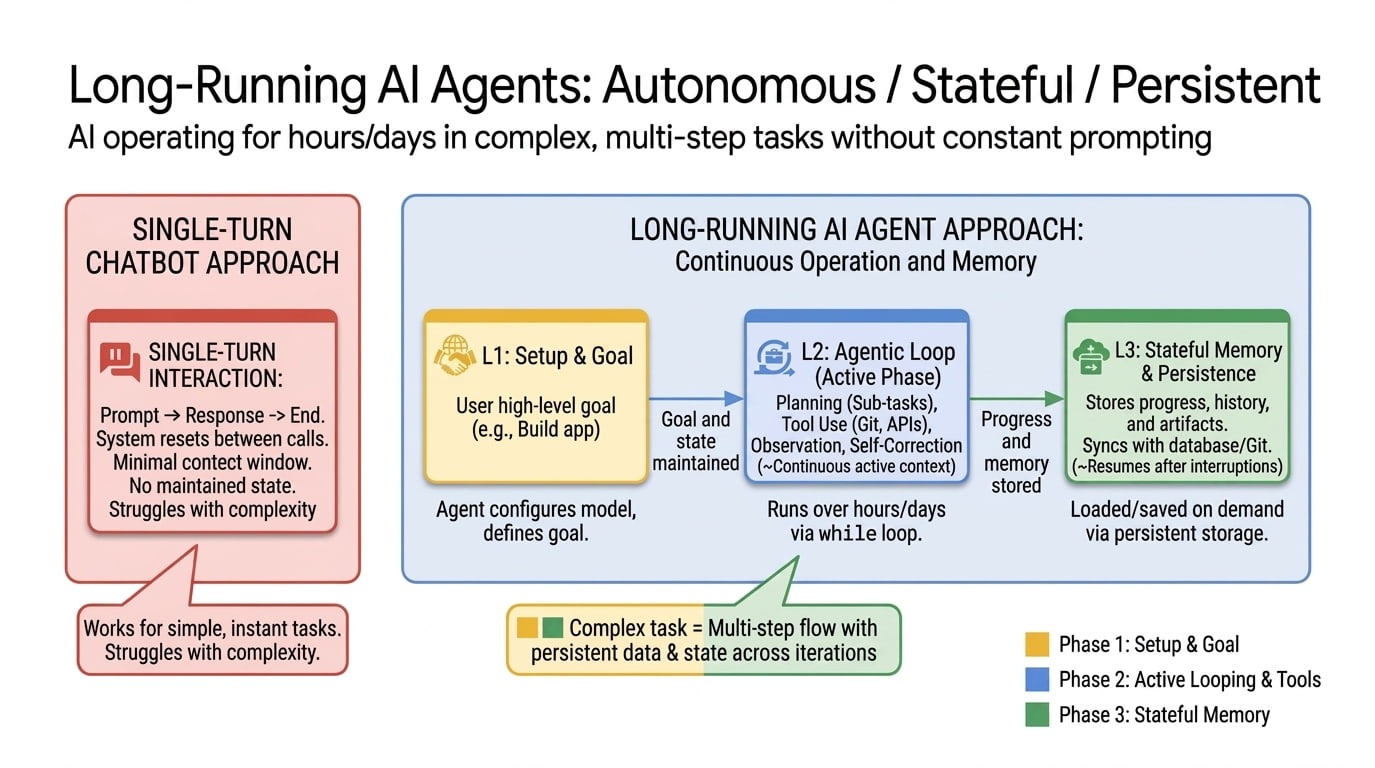
The following article originally appeared on Addy Osmani’s blog and is being reposted here with the author’s permission. A long-running AI agent can keep making progress over hours, days, or weeks. It can do this across many context windows and sandboxes, recover from failure, leave structured artifacts behind, and resume where it left off. For […]

O'Reilly Radar — AI/ML
Evals in Laravel: How to Prove Your AI Output Is Actually Good

Evals in Laravel: How to Prove Your AI Output Is Actually Good

Your Agent::fake() tests prove your Laravel AI feature runs — not that its output is any good. This evals a real ticket classifier with the AI SDK: a golden dataset for the fields you can check, an LLM-as-judge for the free text you can't, and a regression gate that catches a bad prompt before your customers do. Read more

Freek Van der Herten
datasette-agent-edit 0.1a0

datasette-agent-edit 0.1a0

Release: datasette-agent-edit 0.1a0 I'm planning several plugins for Datasette Agent which can make edits to existing pieces of text - things like collaborative Markdown editing, updating large SQL queries, and editing SVG files. Agentic editing of text is a little tricky to get right. My favorite published design for this is for the Claude text editor, which implements the following tools: view - view sections of a file, with line numbers added to every line. str_replace - find an exact…

Simon Willison's Weblog
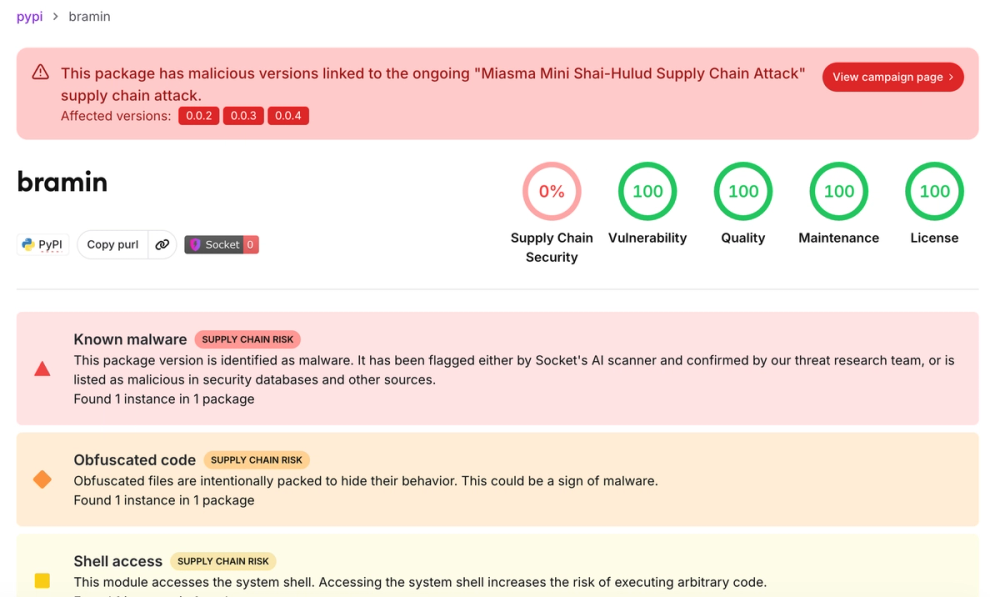
Shai-Hulud Descends to Hades: Miasma Worm Campaign Spreads with New PyPI Wave

Shai-Hulud Descends to Hades: Miasma Worm Campaign Spreads with New PyPI Wave

Socket detected a coordinated PyPI compromise involving 37 malicious wheel artifacts across 19 packages. The compromised releases shipped a *-setup.pth file that attempts to execute automatically during Python startup, download the Bun JavaScript runtime, and run an obfuscated JavaScript payload named _index.js. Socket’s AI malware detection system identified the malicious package cluster minutes after publication. The attack is cross-runtime, and the tradecraft is unmistakably Shai-Hulud /…

Socket
Running Python code in a sandbox with MicroPython and WASM

Running Python code in a sandbox with MicroPython and WASM

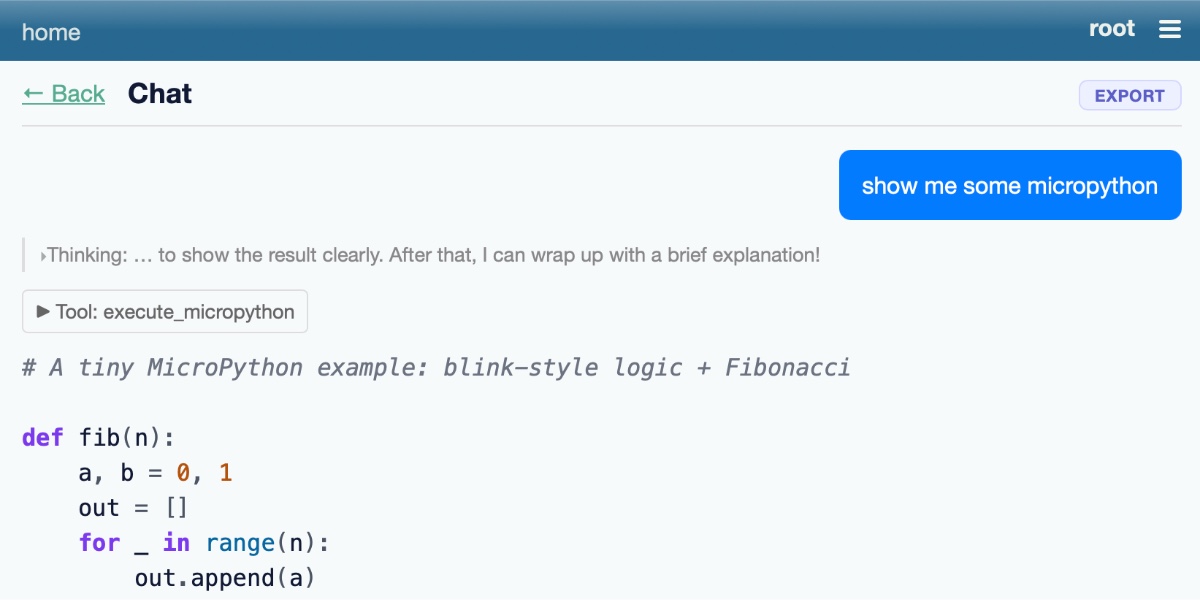
I've been experimenting with different approaches to running code in a sandbox for several years now, but my latest attempt feels like it might finally have all of the characteristics I've been looking for. I've released it as an alpha package called micropython-wasm, and I'm using it for a code execution sandbox plugin for Datasette Agent called datasette-agent-micropython. Why do I want a sandbox? What I want from a sandbox WebAssembly looks really promising here MicroPython in WebAssembly…

Simon Willison's Weblog
OpenAI Help: Lockdown Mode

OpenAI Help: Lockdown Mode

OpenAI Help: Lockdown Mode OpenAI first teased this in February, but now it's live and "rolling out to eligible personal accounts, including Free, Go, Plus, and Pro, and self-serve ChatGPT Business accounts": Lockdown Mode is designed to help prevent the final stage of data exfiltration from a prompt injection attack by limiting outbound network requests that could transfer sensitive data to an attacker. Lockdown Mode does not prevent prompt injections from appearing in the content ChatGPT…

Simon Willison's Weblog
Esc