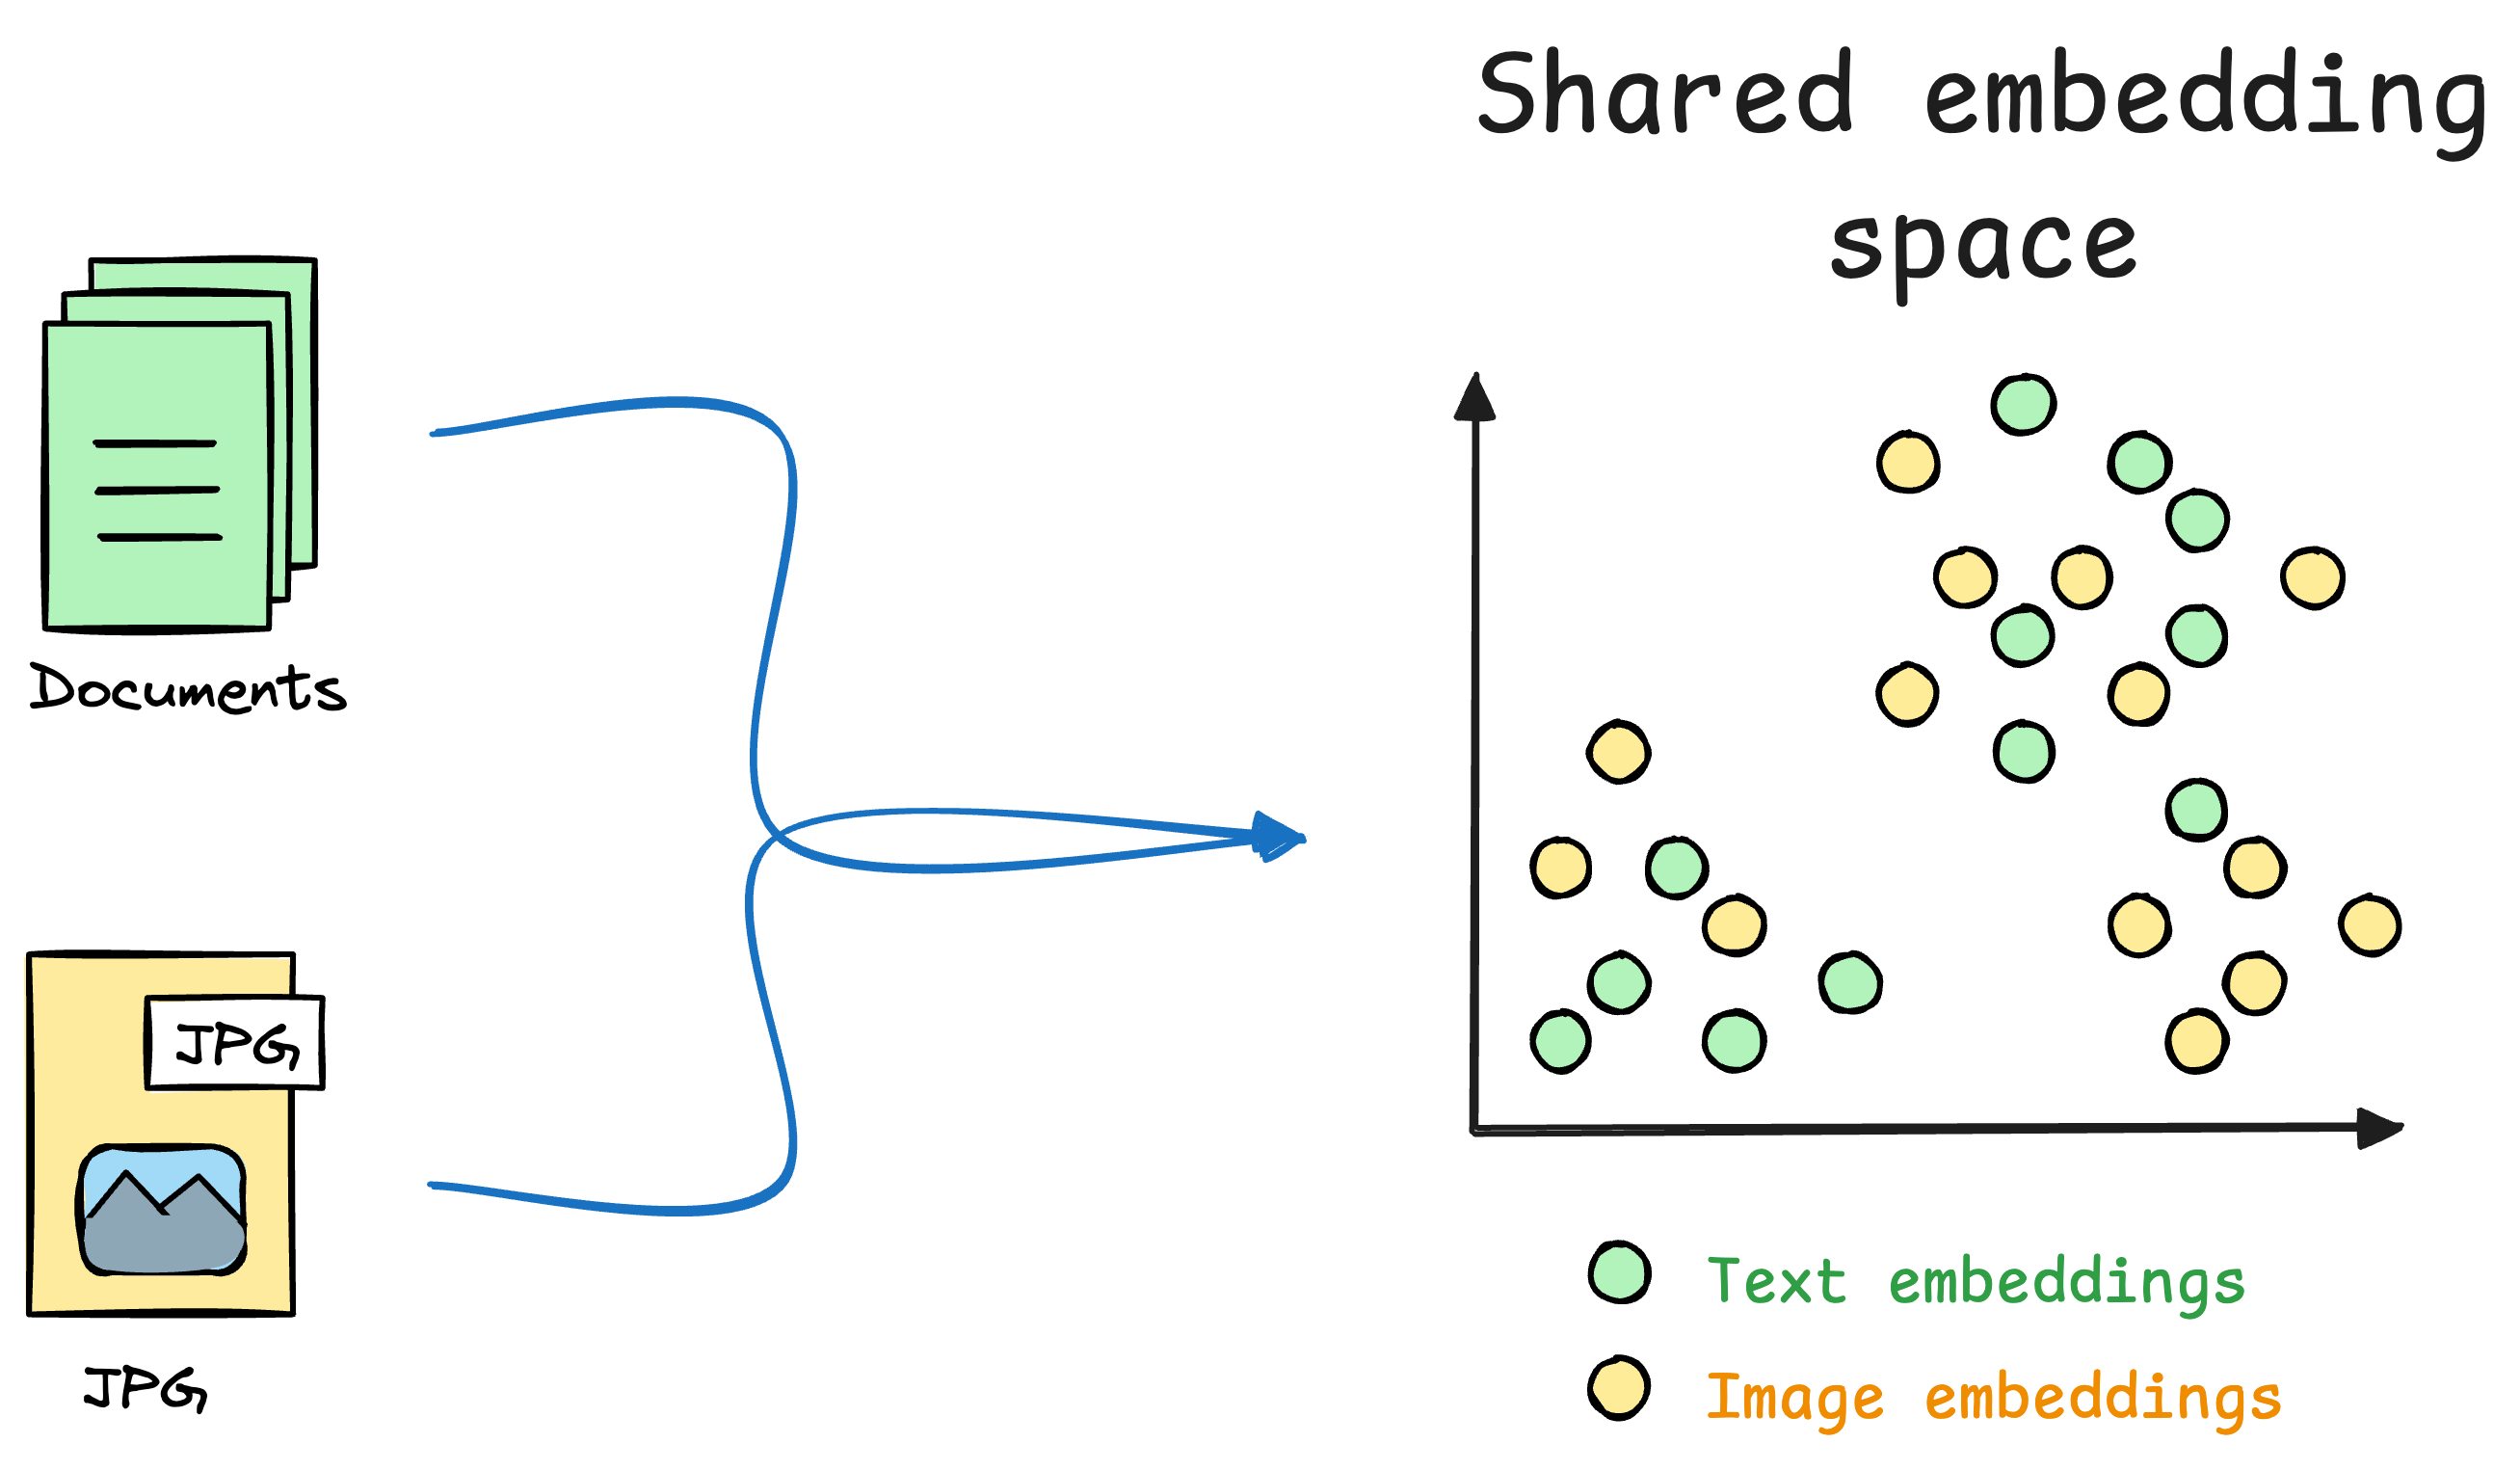
Implementing a Siamese Network with Contrastive Learning
Full guide with code.
Lire
Full guide with code.

Ten malicious versions were published with valid npm provenance after a threat actor abused a comment-triggered GitHub Actions publishing workflow, with the latest release still compromised at the time of writing. The Socket Threat Research Team is investigating an ongoing Mini Shai-Hulud compromise, affecting the npm package @7nohe/openapi-react-query-codegen. On August 28, 2026, ten malicious versions were published in two waves roughly twenty minutes apart, spanning every maintained release…

OpenAI is mobilizing a collective response to the rapidly increasing capabilities of AI models and the rising threat of autonomous, machine-speed cyberattacks. In an effort to rally global defenses, a coalition of more than 100 technology, cybersecurity, and financial organizations, including Google, Microsoft, Anthropic, AWS, Cloudflare, and CrowdStrike, has signed an open letter calling for a surge in defenses. Socket signed because software supply chain security requires industry-wide…

Today, Socket is expanding browser extension security to Microsoft Edge. Enterprise security teams can now evaluate extensions published through Microsoft Edge Add-ons and monitor new releases for malicious behavior, excessive permissions, data collection, suspicious infrastructure, and changes that introduce new risk. This brings the same code and behavioral analysis already available for Chrome and Firefox to Microsoft’s extension ecosystem. Socket examines what an extension can access, what…
The following article originally appeared on Tim O’Brien’s Medium blog and is being republished here with the author’s permission. AI costs are easy to count and hard to understand, and judging effort by a token volume? While that might feel like a valid measure of value or complexity, it doesn’t capture the details that define […]

[[Writing]] has become my passion over time; I have built a whole company based on technical writing services (even though most say that’s impossible). After doing it for 11 years publicly (much longer privately), I still enjoy it every day. If I could have one dream, I’d probably imagine the book-author lifestyle, where I go to a faraway place or island and just write in my journal, articles from my vast notes system (~3 million words, or 2-3 books.
🎙️ PHP Podcast – August 27, 2026 Hosts: Joe Ferguson, Sara Golemon & Holly Schilling Zero-downtime swaps that nobody noticed, 3D printers that refuse to calibrate, a nostalgia tour through the entire PHPArch back catalog, Go generics, TypePHP, and a very good reason to book a flight to Belgium. This one lived in the gutter […] The post The PHP Podcast 2026.08.27 appeared first on PHP Architect.
Breaking Claude Code Opus 5 Auto Mode Anthropic are putting a great deal of faith in Claude Code's auto mode for protecting their coding agent users against prompt injection attacks. They recently made that the default and have made bold claims about its effectiveness. Johann Rehberger is one of the most credible prompt injection researchers active today. He found an attack against auto mode which he claims works 80% of the time, by tricking Claude Code into downloading and uncompressing a zip…
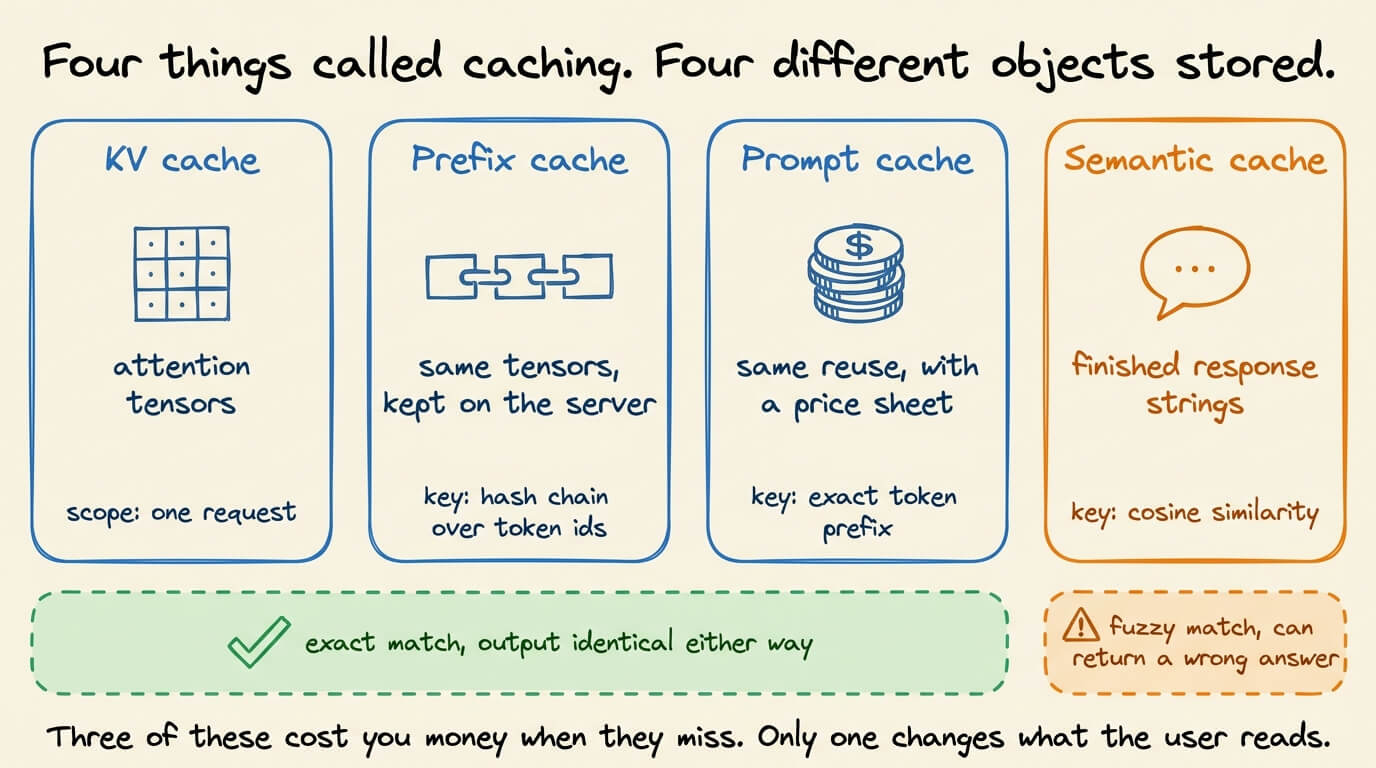
...explained with best practices in production.

Socket identified 19 malicious extensions published in the last six months, delivering an extendable malware framework. Identified malware samples create WebSocket communication channel with command and control (C2) server, perform CSP stripping and abuse XSS injection to trigger execution of malicious payloads previously downloaded from the C2 server. Malicious capabilities are primarily focused on, but not limited to, wallet secret stealing and crypto draining. The most impactful tactic is…
A lot of professional writers say they never do it. And for writers who do, the consequences can be serious. Book contracts have been withdrawn. People have lost jobs. I have a contrarian view. I say AI is a medium, like painting, sculpture, photography, music, or language itself. If AI is a medium, it is […]
For a decade, identity and access management meant one thing: governing the humans who log in. Employee joins, gets provisioned, gets a manager, gets a departure date, gets offboarded. That loop is well understood. What changed is that the fastest-growing population inside enterprise environments is no longer human, and the governance playbook written for people […]
Qwen3.8-Flash-Next Another open weights model from Qwen. This one is "a multimodal MoE model that also serves as an early preview of the architecture used in Qwen4". It's pretty big: 125B tokens, but only 6B active which means it gets a significant performance boost. I've been trying it out on a DGX Spark using these Unsloth quantized models. I'm still exploring the model - so far I've tried the 72.5GB UD-IQ1_S one (producing these pelicans) and the 78.9GB UD-Q2_K_XL (producing these). My…
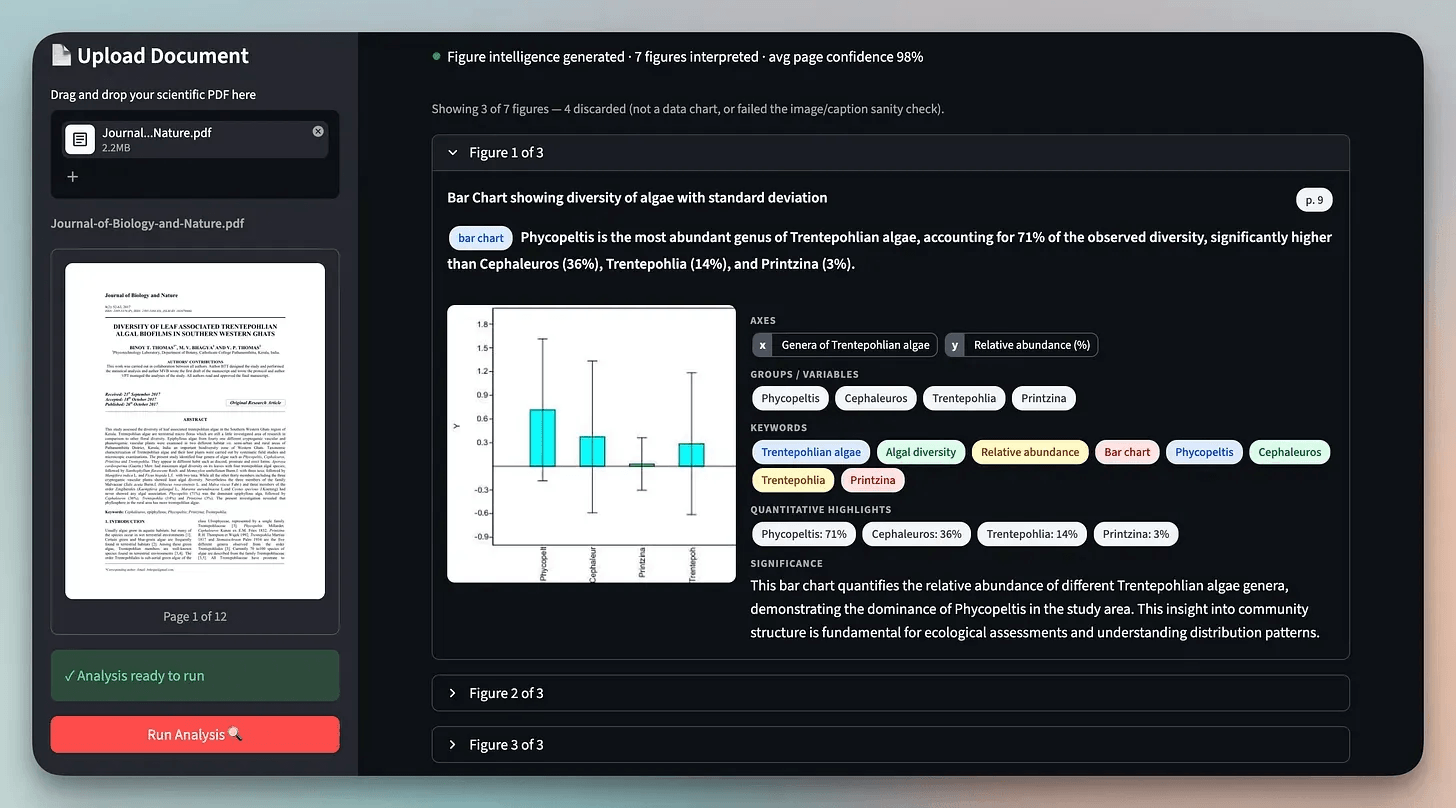
A full walkthrough of the extraction schema, with code.

Today, we’re excited to launch Socket for ClickUp in beta. On the heels of our Socket for Asana release, the new integration gives teams another way to send Socket alerts directly into the tools they already use to manage work. ClickUp brings tasks, docs, whiteboards, and chat into one highly customizable platform. If your organization uses it to organize work, Socket alerts can now become assigned, trackable tasks in the same Lists and workflows your teams already use. Create tasks manually…
Aucun résultat
Essayez avec d'autres termes de recherche.