/
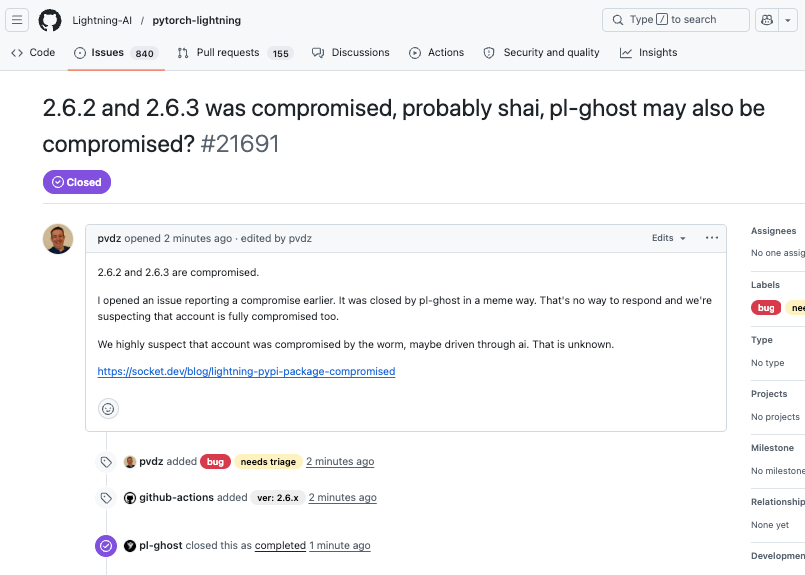
lightning PyPI Package Compromised in Supply Chain Attack
The popular PyPI package lightning has been compromised in a supply chain attack affecting newly published versions of the package. Socket has classified lightning versions 2.6.2 and 2.6.3 as malicious. Version 2.6.1, published on January 30, 2026, is clean. Version 2.6.2, published on April 30, 2026, introduced malicious code into the legitimate library. Socket’s AI scanner flagged both versions 2.6.2 and 2.6.3as potentially malicious eighteen minutes after publication. The compromise affects…
Lire
Laravel Route Binding Behind the Curtains
A deep dive into how Laravel transforms raw route segments into models, scoped children, enums, and custom bound values before your controller runs. Read more
Lire
AI Code Review Only Catches Half of Your Bugs
This is the fifth article in a series on agentic engineering and AI-driven development. Read part one here, part two here, part three here, and part four here. I recently had a taste of humility with my AI-generated code. I live in Park Slope, Brooklyn, and recently I needed to get to the other side of the neighborhood. […]
Lire
The Zig project's rationale for their firm anti-AI contribution policy
The Zig project's rationale for their firm anti-AI contribution policy
Zig has one of the most stringent anti-LLM policies of any major open source project: No LLMs for issues. No LLMs for pull requests. No LLMs for comments on the bug tracker, including translation. English is encouraged, but not required. You are welcome to post in your native language and rely on others to have their own translation tools of choice to interpret your words. The most prominent project written in Zig may be the Bun JavaScript runtime, which was acquired by Anthropic in December…
Lire
llm 0.32a1
llm 0.32a1
Release: llm 0.32a1 Fixed a bug in 0.32a0 where tool-calling conversations were not correctly reinflated from SQLite. #1426 Tags: llm
Lire
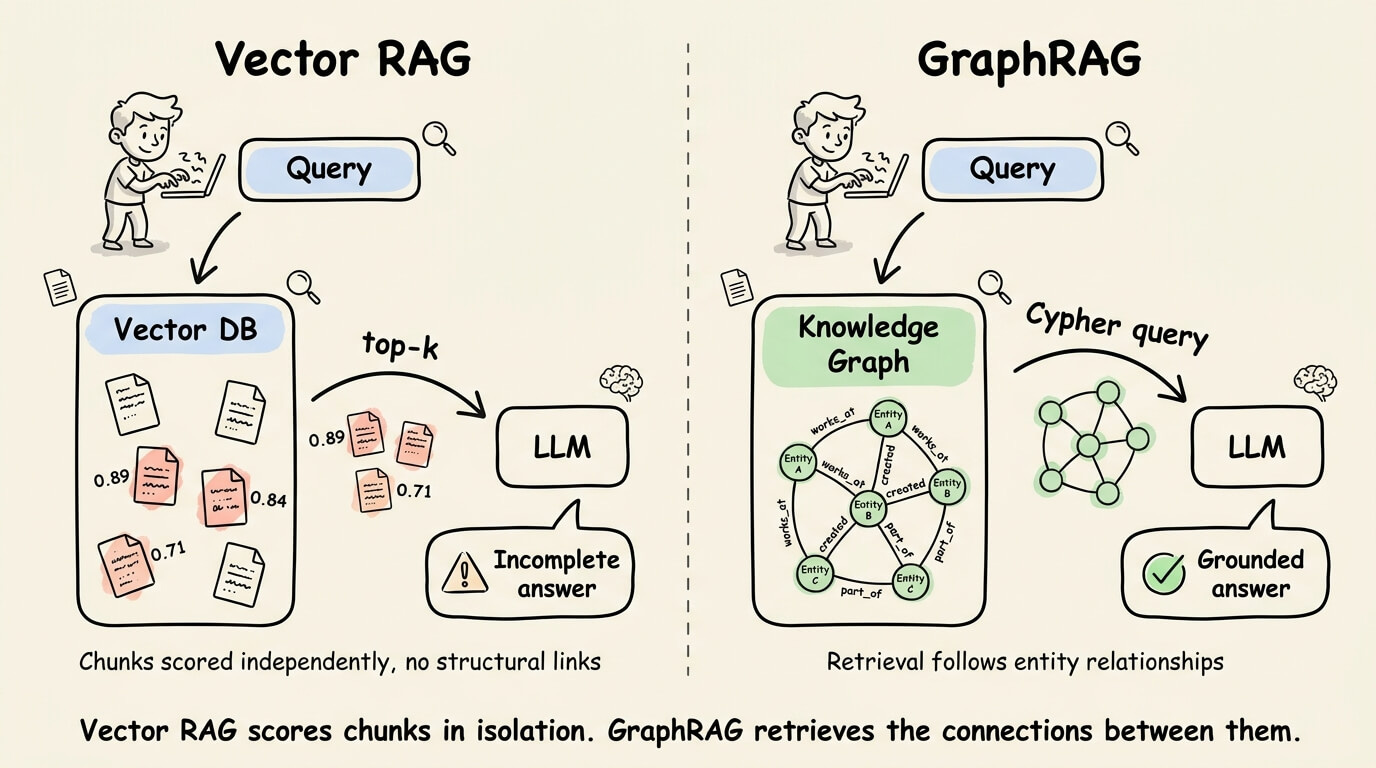
[Hands-on] Build OpenClaw’s Core In a Single Visual Workflow
...using 100% open-source stack!
Lire
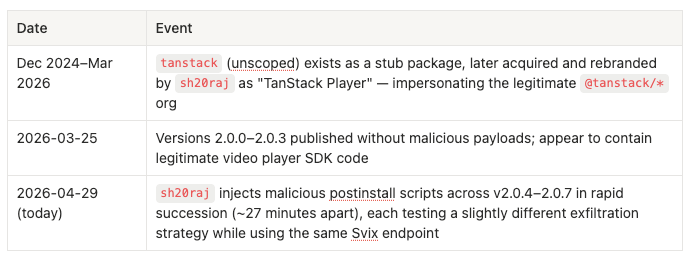
Malicious npm Package Brand-Squats TanStack to Exfiltrate Environment Variables
The Socket Research Team has detected an active supply-chain attack targeting the unscoped tanstack package on npm, a brand-squatted impersonation of the legitimate @tanstack/* organization. Beginning today, the package's maintainer (sh20raj) began pushing malicious versions that silently steal environment variable files, including .env, .env.local, and .env.production, from developers' machines at install time, exfiltrating them to an attacker-controlled endpoint. Versions 2.0.4 through 2.0.7…
Lire
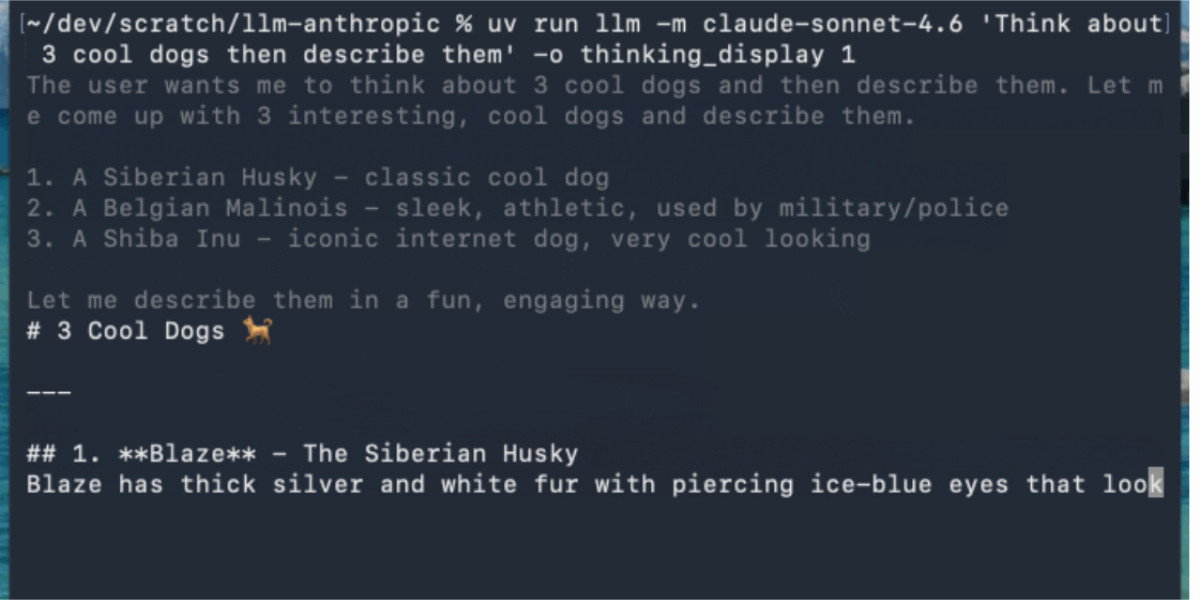
LLM 0.32a0 is a major backwards-compatible refactor
I just released LLM 0.32a0, an alpha release of my LLM Python library and CLI tool for accessing LLMs, with some consequential changes that I've been working towards for quite a while. Previous versions of LLM modeled the world in terms of prompts and responses. Send the model a text prompt, get back a text response. import llm model = llm.get_model("gpt-5.5") response = model.prompt("Capital of France?") print(response.text()) This made sense when I started working on the library back in April…
Lire
llm 0.32a0
llm 0.32a0
Release: llm 0.32a0 See the annotated release notes. Tags: llm
Lire
Three thoughts on the Musk-OpenAI lawsuit
It’s hard to root for either side, but Musk has a point.
Lire
Community Corner: Storyblok with Daniel Mendoza
In this episode, Scott talks Storyblok with Daniel Mendoza and his talk on using AI to help developers learn new technology that he will be presenting at JStek 2026. Links: Our Discord – https://discord.gg/aMTxunVx Buy our shirts – https://store.phparch.com/products/community-corner-podcast-t-shirt Daniel’s Links: LinkedIn – https://www.linkedin.com/in/daniel-mendoza-503396152/ Personal Site – https://danieljmendoza.com/ Scott’s Links: Website – https://scott.keck-warren.com/ Bluesky […] The…
Lire
★ Announcing laravel-sluggable v4 with self-healing URLs
The spatie/laravel-sluggable package has been around for close to a decade. A slug is the readable part of a URL that identifies a record, like announcing-laravel-sluggable-v4-with-self-healing-urls in this post's URL. The package generates one for any Eloquent model when you save it, derived from a title or another text field, and most of the time you don't have to think about it. We just released v4, which adds a few things worth talking about. Let me walk you through them. Generating slugs…
Lire
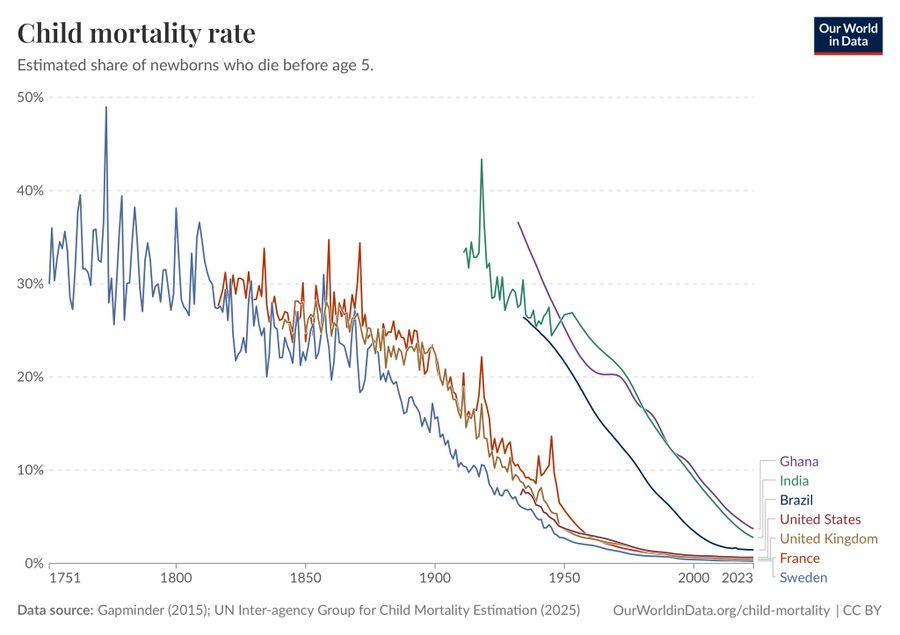
The Most Important Charts In The World
We all need a break so: What is the most important chart in the world?
Lire
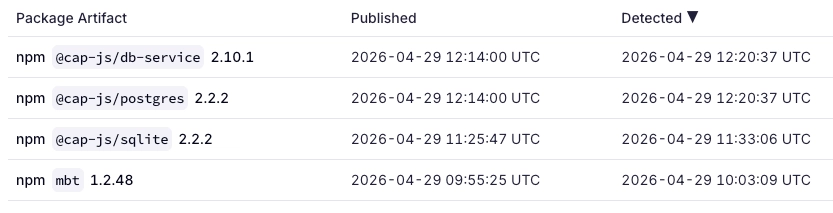
TeamPCP-Linked Supply Chain Attack Hits SAP CAP and Cloud MTA npm Packages
Socket is investigating a suspected supply chain attack affecting multiple npm packages associated with SAP’s JavaScript and cloud application development ecosystem. At the time of publication, Socket has identified the following affected package versions: mbt@1.2.48 @cap-js/db-service@2.10.1 @cap-js/postgres@2.2.2 @cap-js/sqlite@2.2.2 Socket’s analysis indicates that the affected versions introduced new installation-time behavior that was not previously part of these packages’ expected…
Lire
The Zig project's rationale for their firm anti-AI contribution policy
The Zig project's rationale for their firm anti-AI contribution policy
Simon Willison's Weblog •
llm 0.32a1
llm 0.32a0
AI #166: Google Sells Out
lightning PyPI Package Compromised in Supply Chain Attack
Laravel Route Binding Behind the Curtains
AI Code Review Only Catches Half of Your Bugs
The Zig project's rationale for their firm anti-AI contribution policy
llm 0.32a1
[Hands-on] Build OpenClaw’s Core In a Single Visual Workflow
Malicious npm Package Brand-Squats TanStack to Exfiltrate Environment Variables
LLM 0.32a0 is a major backwards-compatible refactor
llm 0.32a0
Three thoughts on the Musk-OpenAI lawsuit
Community Corner: Storyblok with Daniel Mendoza
★ Announcing laravel-sluggable v4 with self-healing URLs
The Most Important Charts In The World
TeamPCP-Linked Supply Chain Attack Hits SAP CAP and Cloud MTA npm Packages
Aucun résultat
Essayez avec d'autres termes de recherche.