Flux
Couleur d'accent
Toutes les catégories

Programmation

3647 articles

Ruff v0.16.0

Ruff v0.16.0

Ruff v0.16.0 Astral shipped a significant new version of their Ruff Python linting tool a few days ago on July 23rd. I noticed today because my various CI jobs all started failing thanks to new default Ruff checks and my unpinned "ruff" dev dependency. From Brent Westbrook's announcement post: Ruff now enables 413 rules by default, up from 59 in previous versions. Since Ruff's default rule set was last modified in v0.1.0, the number of rules in Ruff has grown from 708 to 968. Many of these…

Simon Willison's Weblog
A Card Counter Mindset

A Card Counter Mindset

Summertime and the living is easy…or so they say. July has us fully immersed in the summer season, which is proving to be a hot one for most. Making it the perfect time to find a cool spot in the shade (or air conditioning) and read the July issue. Let’s get started with a preview […] The post A Card Counter Mindset appeared first on PHP Architect.

PHP Architect
Quoting Boris Cherny

Quoting Boris Cherny

More than any of these eval scores, what is most exciting to me is something else: Opus 5 is our least prompt injectable model yet. It is a bit buried in the system card, but across PI evals and red teaming, Opus 5 is very hard to prompt inject successfully. — Boris Cherny, here's that System Card section, page 73 Tags: prompt-injection, anthropic, claude, generative-ai, ai, llms, boris-cherny

Simon Willison's Weblog
Introducing Claude Opus 5

Introducing Claude Opus 5

Introducing Claude Opus 5 I've been offline kayaking with sea otters for much of today so I haven't had a chance to put Anthropic's new model Claude Opus 5 through its paces yet. The buzz is positive, and Anthropic's description of it as a "thoughtful and proactive model that comes close to the frontier intelligence of Claude Fable 5 at half the price" sounds promising. It's currently leading the Artificial Analysis leaderboard, in front of even Fable 5. It's priced the same as Opus 4.8, and…

Simon Willison's Weblog
Fake Corepack Site Distributes Infostealer and Proxyware to Developers

Fake Corepack Site Distributes Infostealer and Proxyware to Developers

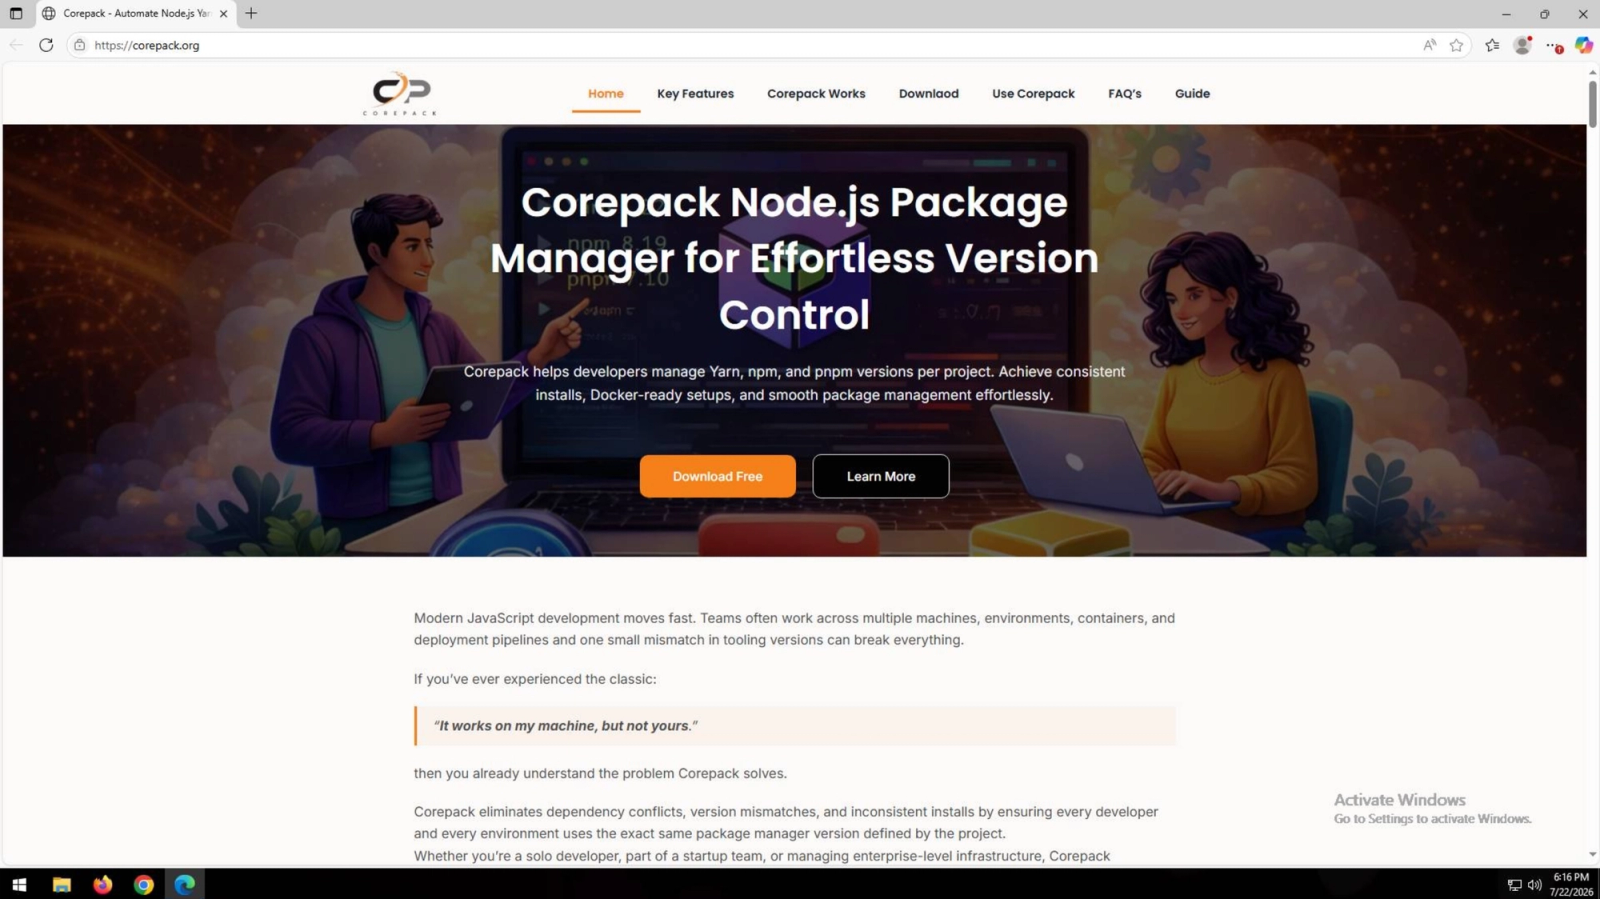
A website at corepack[.]org is impersonating Corepack, the Node.js tool for managing package managers, and using that identity to push malware to developers who land on the page looking for a download. The site has existed in some form since early 2026 as a low-quality, apparently AI-generated imitation, but it recently started serving executable downloads. Socket's Threat Research team analyzed the site and confirmed it as a developer-targeted phishing and impersonation operation that drops an…

Socket
The PHP Podcast 2026.07.23

The PHP Podcast 2026.07.23

🎙️ PHP Podcast – July 23, 2026 Hosts: Joe Ferguson, Sara Golemon, and Holly Schilling Eric got ousted from his own show (no pants required), Holly’s elephants are lost somewhere in the U.S., and the crew talks SIMD, PHP 8.6 feature freeze, and whether AI can actually create. Also, socks. 🩳 A Show Without Pants: […] The post The PHP Podcast 2026.07.23 appeared first on PHP Architect.

PHP Architect
The first known runaway AI agent - or a very bad marketing stunt?

The first known runaway AI agent - or a very bad marketing stunt?

The first known runaway AI agent - or a very bad marketing stunt? Martin Alderson's commentary on the OpenAI accidental cyberattack against Hugging Face includes a couple of details I hadn't considered. First, Hugging Face offers a truly rich target if you're trying to find potential vulnerabilities that require executing arbitrary code: Hugging Face has an enormous attack surface. They have more interfaces than I can count which run untrusted models and code. While they definitely have…

Simon Willison's Weblog
Quoting Seth Larson

Quoting Seth Larson

The Python Package Index (PyPI) now rejects new files being uploaded to releases that are older than 14 days. This restriction was put in place to prevent old and long-stable releases from being poisoned in case publishing tokens or workflows of PyPI projects were compromised. As far as we are aware this has not yet been abused, but there is no technical reason beyond that attackers weren't aware it was possible. — Seth Larson, PyPI blog Tags: packaging, python, supply-chain, pypi,…

Simon Willison's Weblog
Quoting Thomas Ptacek

Quoting Thomas Ptacek

I genuinely believe that if you took an open weights model from 2025 and built a pentest harness for it, it could do this kind of sandbox escape and scan/hack in most networks. This is only surprising because you assume OpenAI has sounder sandboxes. — Thomas Ptacek, doesn't think this even needs a frontier model Tags: thomas-ptacek, openai, security, generative-ai, ai-security-research, ai, llms, sandboxing

Simon Willison's Weblog
Esc