"A" for "Apathy"
Read the full post on https://stitcher.io/blog/a-for-apathy
Lire
Read the full post on https://stitcher.io/blog/a-for-apathy
ChatGPT search now uses the site:operator at scale Promptwatch is part of the emerging "GEO" space, for Generative Engine Optimization - the chatbot version of SEO, where companies offer tools and consulting to help your site increase its presence in replies to prompts inside tools like ChatGPT. The Promptwatch product uses automation to track responses to prompts across end-user chat products like ChatGPT, Claude, and Gemini. They publish aggregate reports on this as part of their own content…
🎙️ PHP Podcast – August 20, 2026 Hosts: Joe Ferguson, Sara Golemon & Holly Schilling Shirley MacLaine is the answer — but what’s the question? RAM prices went up 500%, GitHub fell over for eight hours, and the crew figured out how you can actually contribute to PHP. Glasses optional. 🎬 Shirley MacLaine, Green Room […] The post The PHP Podcast 2026.08.20 appeared first on PHP Architect.
In this episode, Scott talks with Daniel Scherzer, release manager for PHP 8.5 and PHP 8.6, about the bug-fix release cycle, partial function application coming in 8.6, and his upcoming talks at Longhorn PHP on what’s new in 8.6 and building PHP extensions in Rust. Links Our Discord – https://discord.gg/aMTxunVx Buy our shirts – […] The post Community Corner Podcast: PHP 8.5 + 8.6 Release Manager Daniel Scherzer appeared first on PHP Architect.
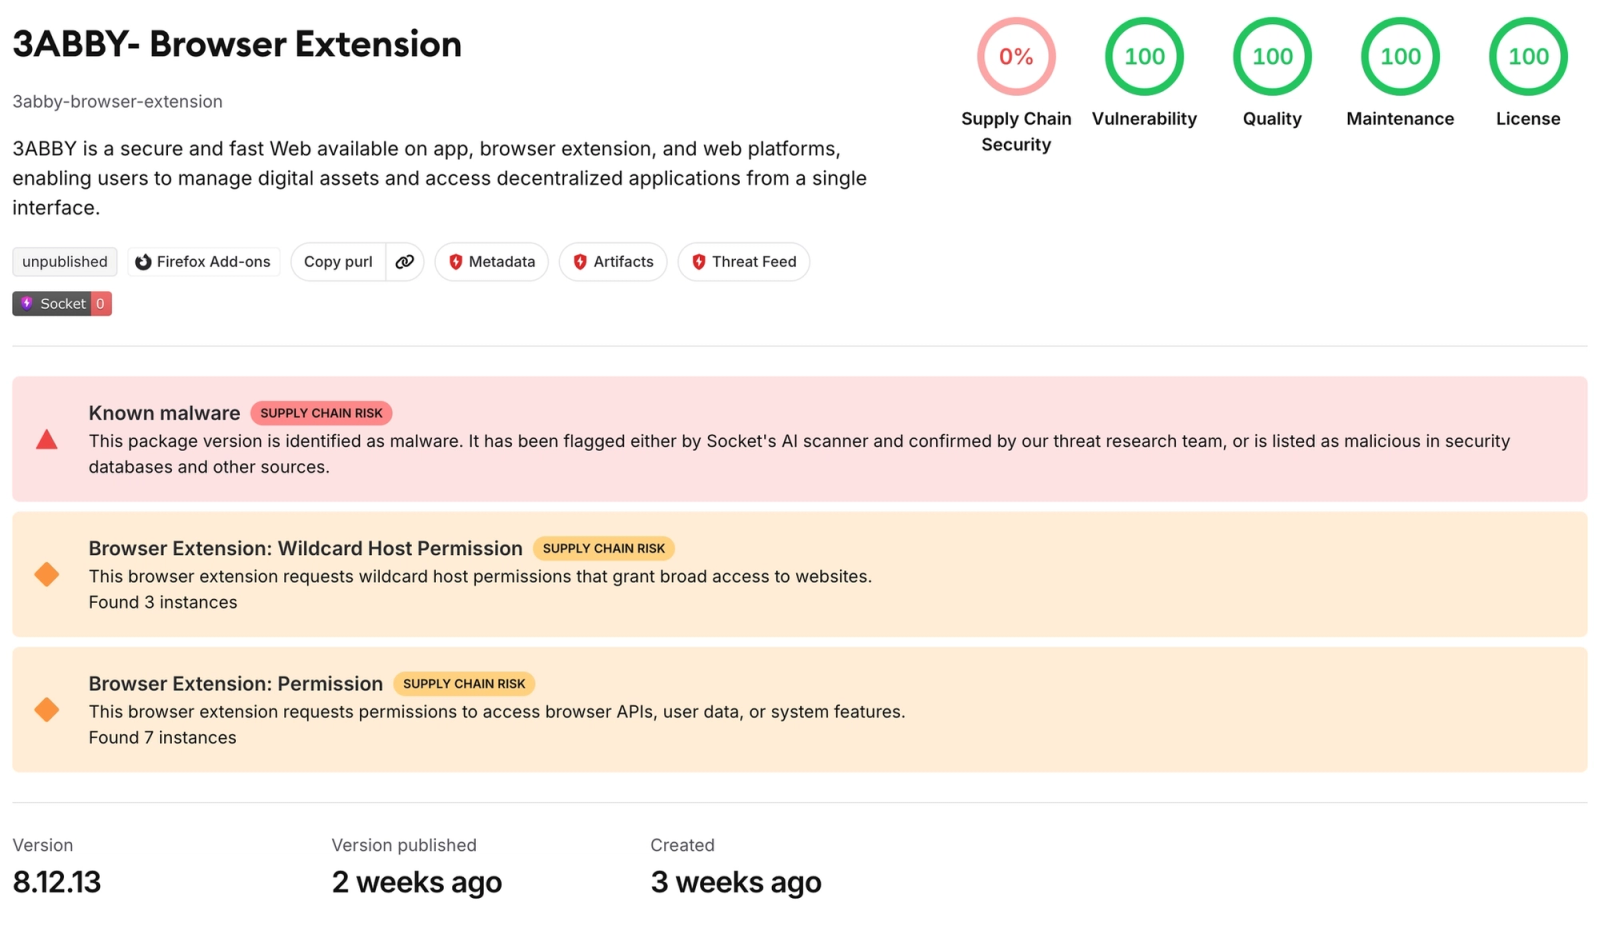
Today, Socket is expanding its browser extension security coverage to Firefox, giving security teams visibility into the extensions used across their organizations and helping them identify malicious behavior, excessive permissions, data collection, suspicious infrastructure, and risky changes between versions. Socket now proactively scans every Firefox extension listed in Mozilla's official addons.mozilla.org directory. At the time of publication, Mozilla's public API lists 97,100…
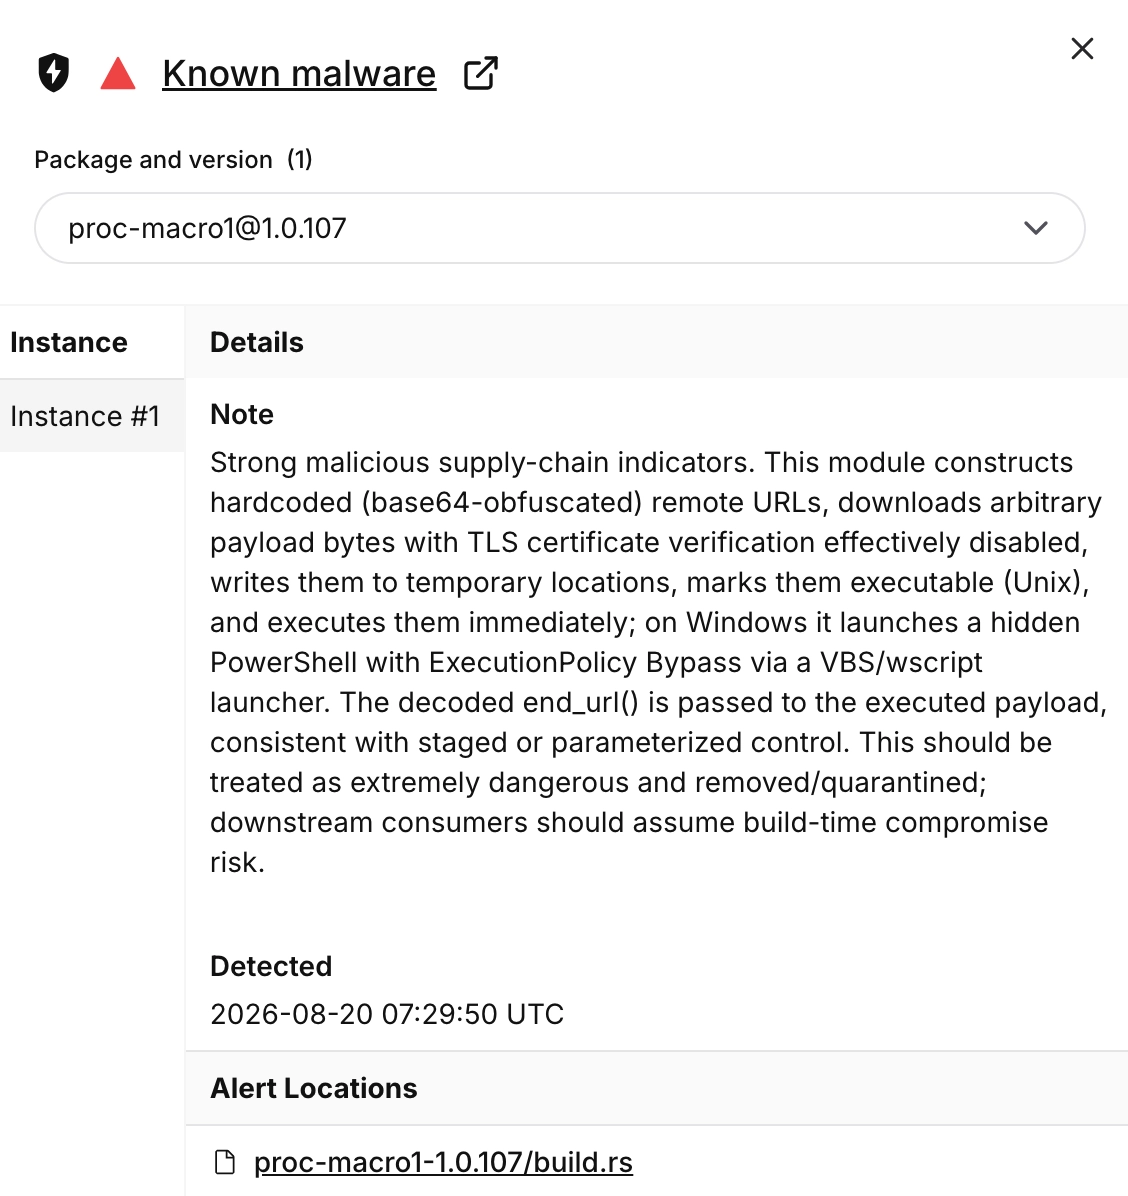
A threat actor compromised legitimate Rust crates and injected a malicious proc-macro1 dependency that executed cross-platform malware automatically during Cargo builds. Socket’s Threat Research Team analyzed a coordinated supply chain attack affecting three legitimate Rust crates maintained by David Roundy (droundy): arrayref@0.3.10 internment@0.8.7 append-only-vec@0.1.9 Socket’s AI Scanner independently detected the malicious proc-macro1 crate on August 20, 2026 at 07:29:50 UTC. At that point…
Research: A shot-scraper-style JSON API on Bun 1.4's new Bun.WebView Today saw the long awaited release of Bun 1.4, the first stable version since the infamous Rust rewrite a few months ago. Interestingly, the Rust rewrite was downplayed in the release notes, which introduced a bewildering array of new features and claimed 2,900 additional bug fixes: Bun 1.4 adds +1,517 tests from the Node.js test suite - our biggest jump in Node.js compatibility since Bun 1.0. Bun v1.4 also fixes over…
A deep dive into modular monoliths, from module APIs and database ownership to cross-module communication, architecture tests, incremental migration, and the signals that justify microservices. Read more
Read the full post on https://stitcher.io/blog/summer-chaos
Research: smolmachines / smolvm as a sandbox for untrusted Python & JavaScript I tasked Claude Fable 5 running in Claude Code for web with the following research task: Put https://smolmachines.com through its paces as a fast secure sandbox. Explore what it would take to use this to run untrusted Python and JavaScript code in a way that is limited in what RAM and CPU time it can take up (protection against "while true") with no network access and filesystem access only to designated files…
My hypothesis is that there is a new opportunity for Extensible Software on the web. LLMs radically lower the cost of authoring extensions, and modern sandbox primitives lower the deployment cost and provide good security boundaries. We can build our app as a solid, accountable core, and allow users to safely extend it in many directions by having LLMs fill in the missing pieces. We can give our users super powers. — Jeremy Morrell, Extensible Software in the age of LLMs Tags: sandboxing,…
Last week I recorded an episode of the Talking Postgres podcast with Claire Giordano on the subject of "How AI is changing software development". We had a really great conversation. Here are a couple of my highlights from a lightly edited transcript (prompt to Claude: "very minor edits to remove disfluencies"). This is the latest version of an argument I've been trying to build about why sometimes it does make sense to talk about lines of code as an indicator of productivity with coding agents,…
Our first feature article this month is ‘I Built a CakePHP Plugin From My iPhone While Packing for a Trip’ by Jamison Bryant. So often an idea pops into our heads, and we think we’ll get to it later when we have time. However, it’s often the case that the time never magically appears to […] The post CakePHP with iPhone appeared first on PHP Architect.
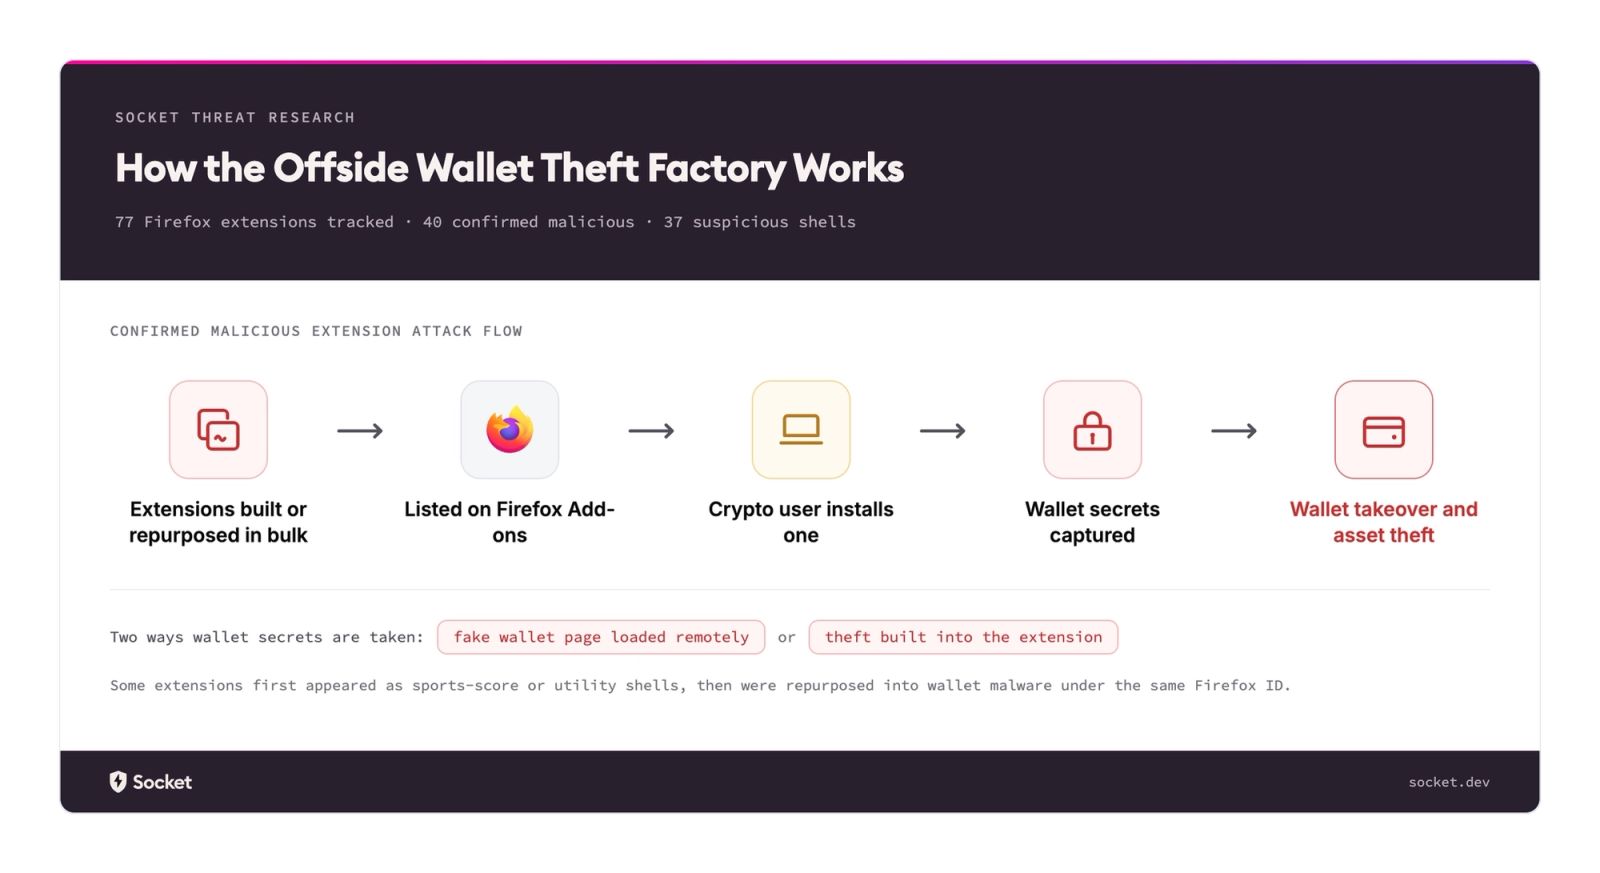
Socket identified 40 malicious extensions that steal wallet secrets or credentials, plus 37 deceptive sports-score shells linked through shared code, infrastructure, publishing artifacts, and version histories. The Socket Threat Research team is tracking 77 Firefox extension identities linked through code reuse, cloned extensions, deceptive marketplace descriptions, author-selected add-on ID patterns and domain-like suffixes, cryptocurrency-wallet impersonation, and version histories showing…

Reprise 0.8.0 is out, a few weeks after the project was introduced on this blog. This release brings back an Encore behavior that some codebases depend on: copied files that keep a stable path on disk. It also fixes a manifest discrepancy between Vite and…